Controlled Unclassified Information
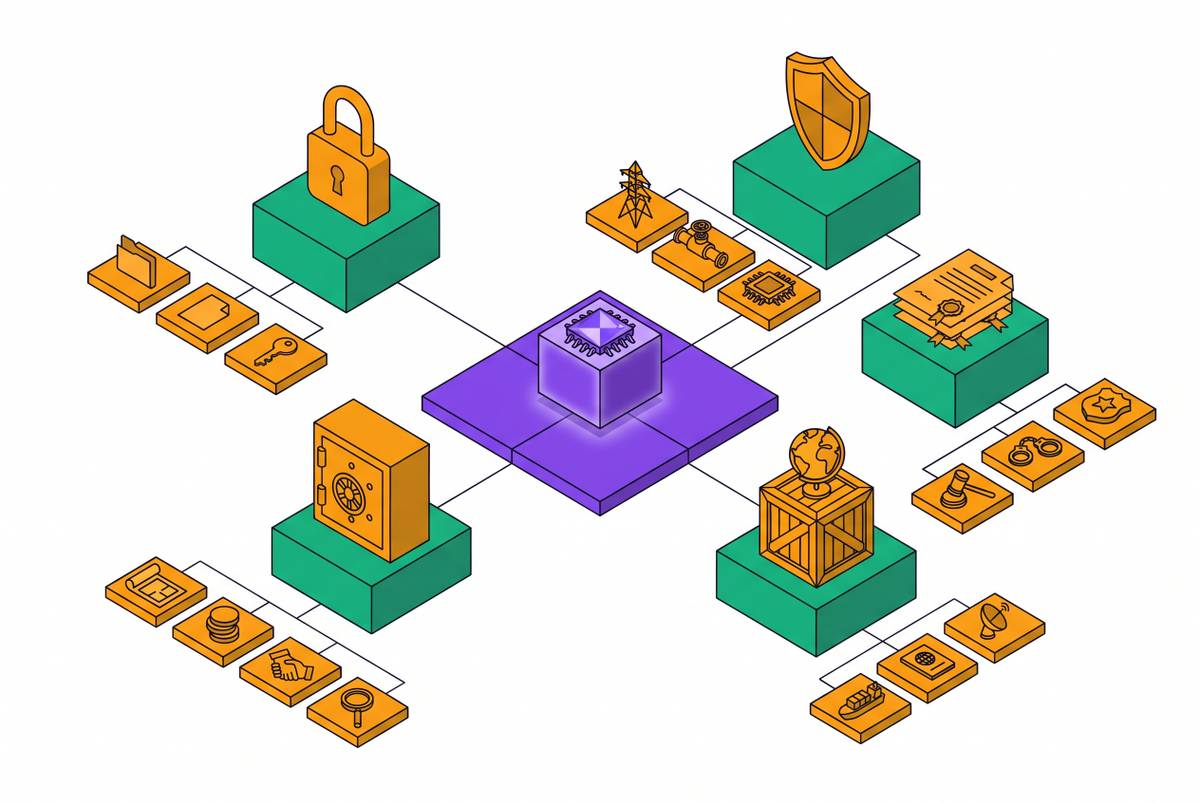
CUI Categories and Subcategories Relevant to AI Systems
AI systems can combine CUI fragments into disclosures source documents never intended.
Marcus Delacroix-Ng
· 9 min read
AI systems can combine CUI fragments into disclosures source documents never intended.
Vendors must document AI agent capabilities, identities.
Organizations running MCP servers must prove they control access, risk, and oversight in production.
Organizations must map AI agent identities and actions to NIST 800-171 controls for assessment.
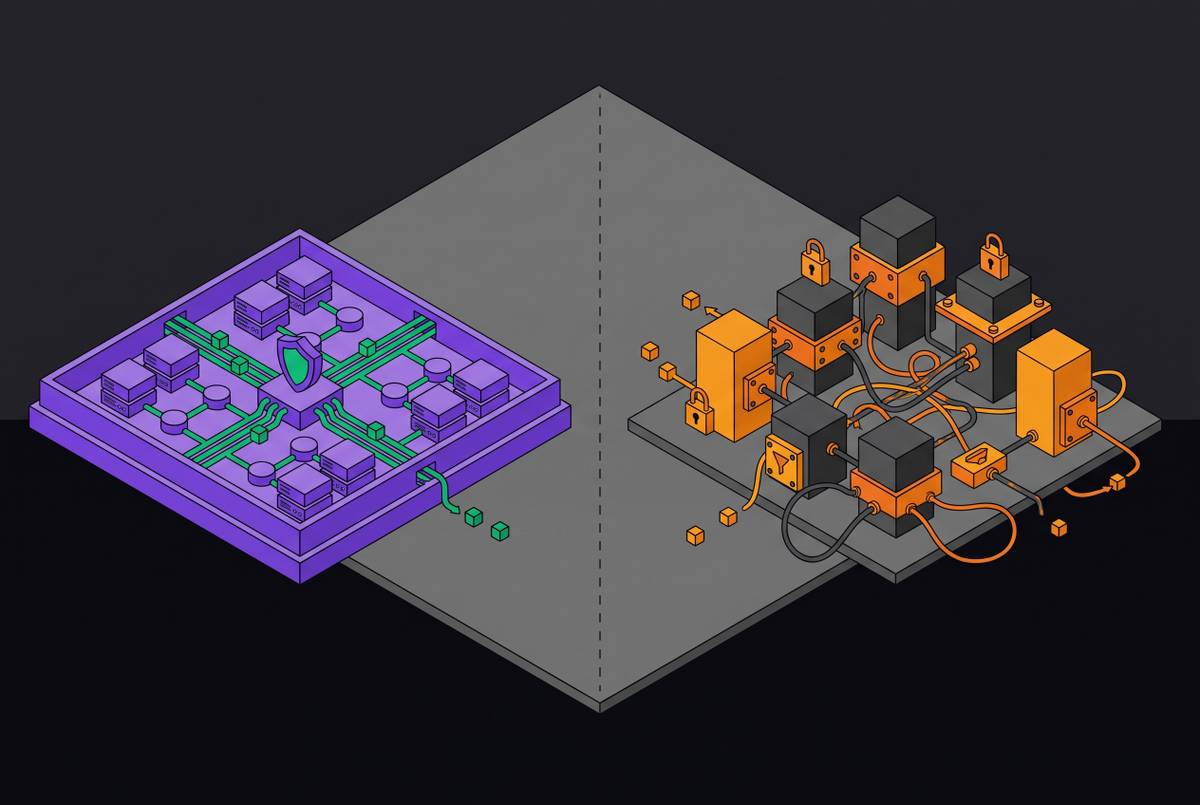
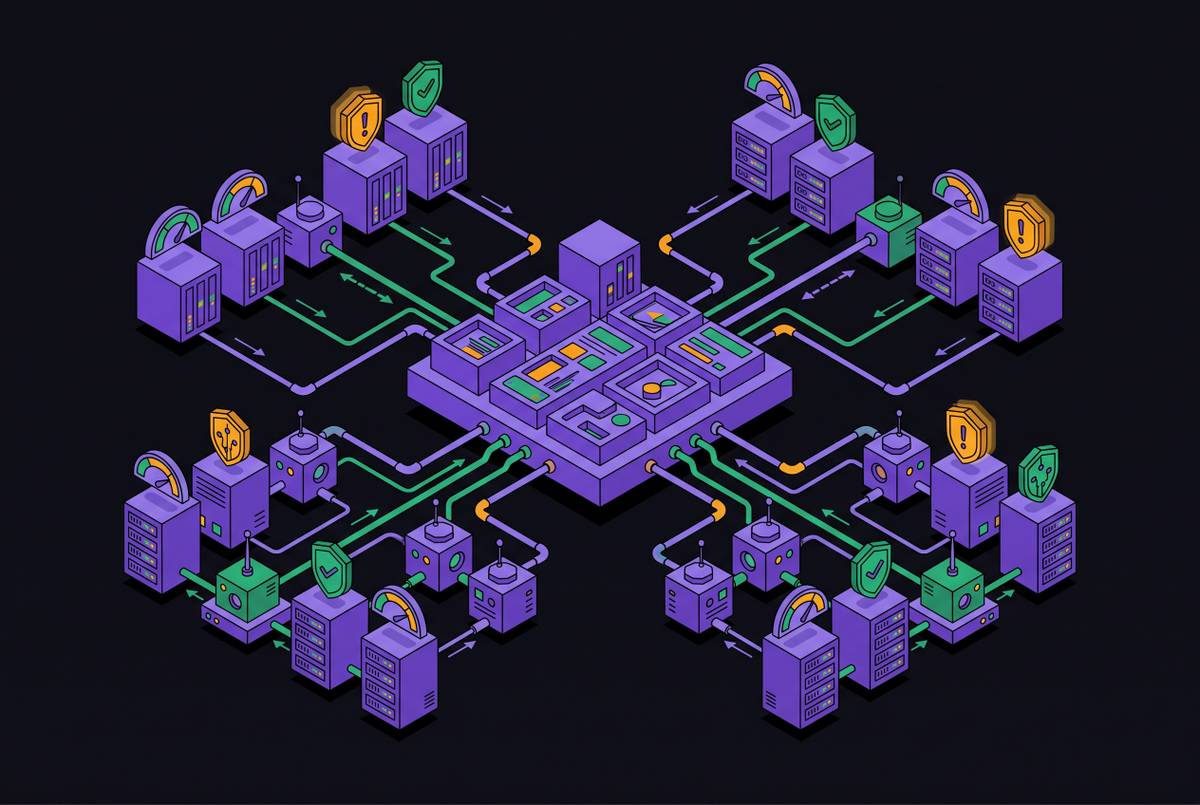
A centralized gateway enforces consistent MCP access policy across all servers and teams.
Purpose-built governance platforms enforce MCP access controls where agents act.
A structured registry and review process makes approved MCP access easier than shadow workarounds.
Production agents need runtime checks that catch malicious MCP servers mid-execution.
Enterprise contracts bar model training, while consumer plans allow it by default.
SaaS contracts must shift governance controls to vendors as AI agents act without human review.
Civilian contractors now must meet strict federal safeguards for sensitive unclassified data.
AI agents need distinct identities to enforce data access limits that match their purpose.