Evaluating Purpose-Built MCP Governance Platforms Against Patchwork Privacy Tooling for Agentic Workflows
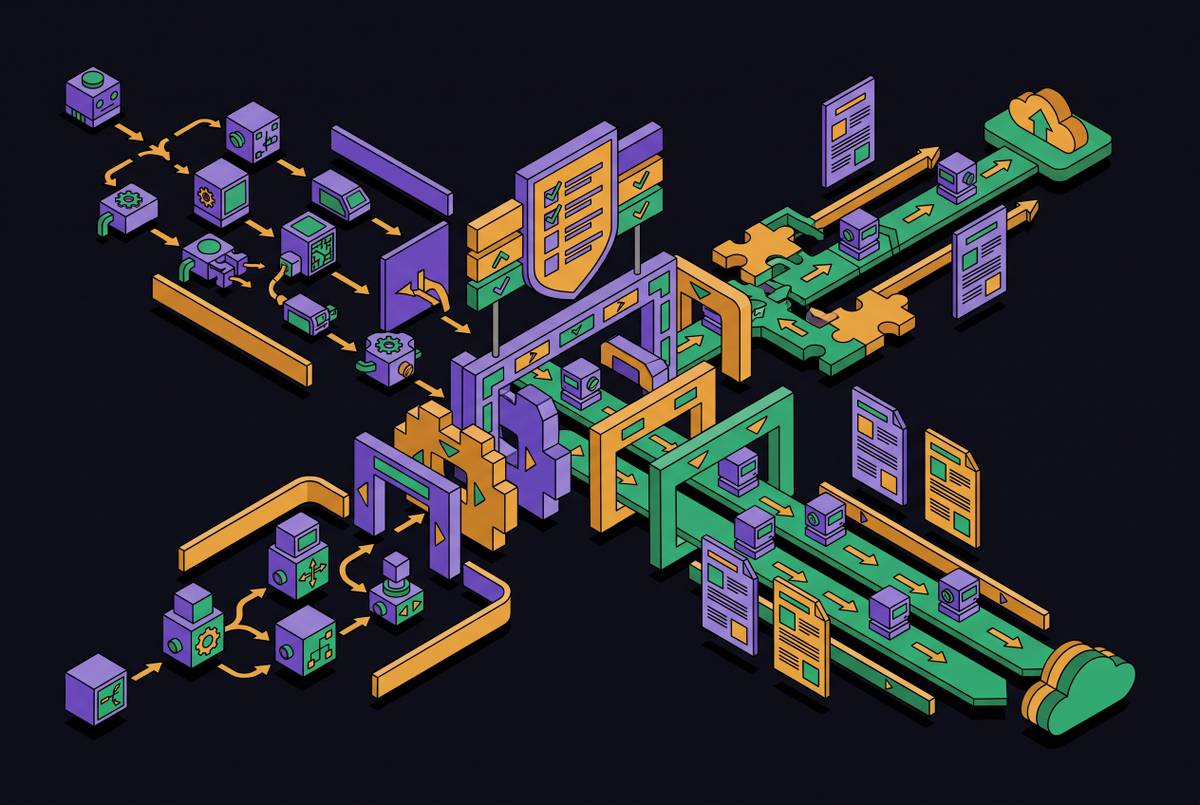
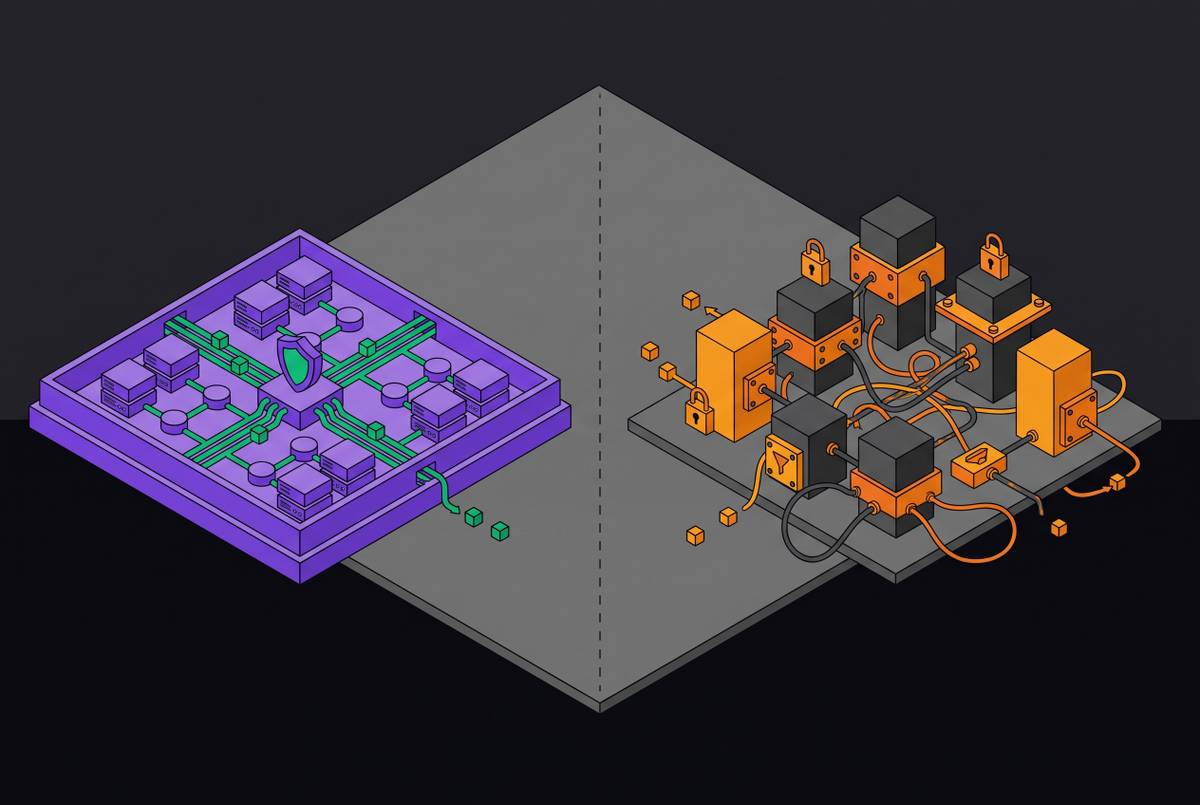
Purpose-built governance platforms enforce MCP access controls where agents act.
Marcus Delacroix-Ng
Section
10 stories in MCP Policy and Compliance.
Purpose-built governance platforms enforce MCP access controls where agents act.
Each tool call needs its own lawful basis check, not one blanket permission for the entire agent.
Governance policies and audit tools make MCP agent deployments GDPR-compliant and accountable.
Agents need runtime governance because MCP shifts compliance decisions from code to behavior.
EU regulators are enforcing NIS2 on AI systems whether the directive names them or not.
Overlooked transfer paths in AI agent traffic create new compliance blind spots.
Build HIPAA compliance into the MCP server layer itself, not downstream from the model.
Autonomous agents break SOC 2's core assumption that humans control each action.
MCP servers expose personal data to unauthenticated access without the lawful bases GDPR demands.
Existing compliance obligations bind agent deployments now, not at the December 2027 deadline.