 AI Observability & Audit Trails
OpenTelemetry Integration With MCP Agent Pipelines
W3C trace context and OpenTelemetry conventions link agent and tool traces.
Priya Subramaniam·
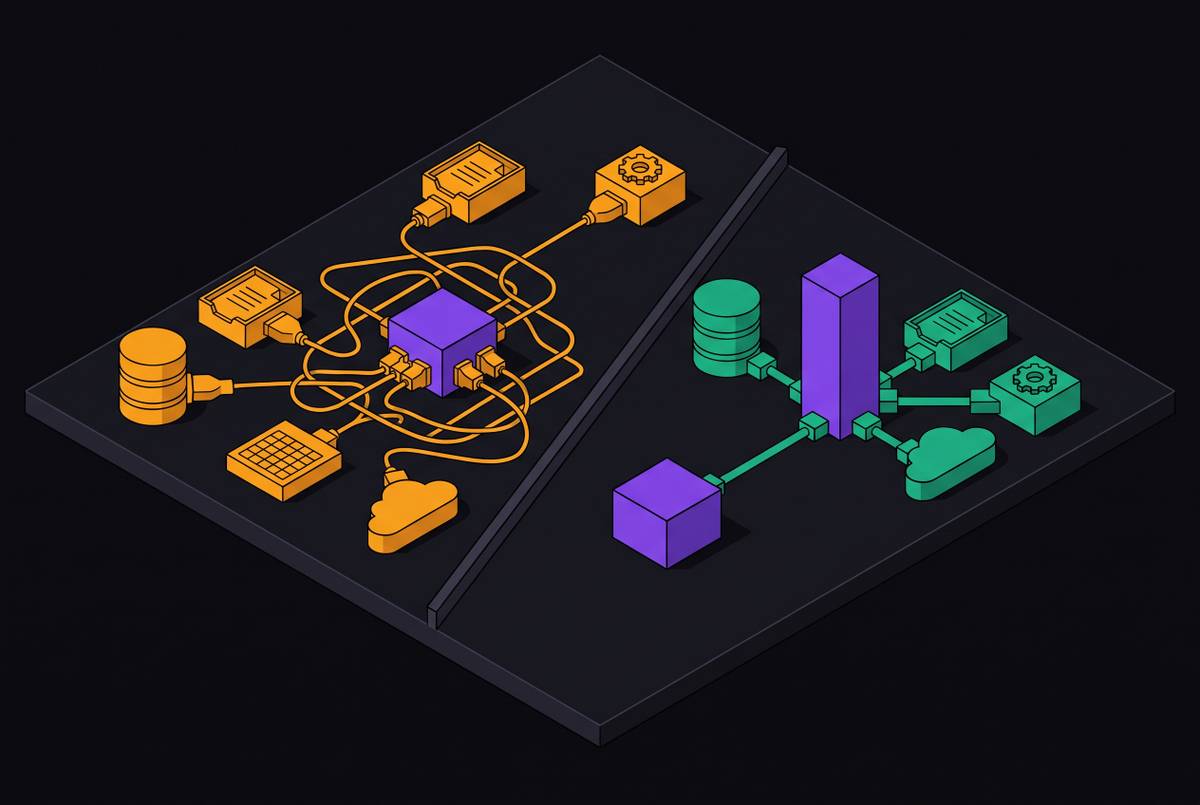 MCP Architecture
MCP Server vs API for Enterprise Tool Integration
MCP discovers tools at runtime; REST handles predictable workflows both need governance.
Priya Subramaniam·
 AI Agent Governance
Agentic AI Guardrails Implementation Patterns
Controls must sit in the agent's execution path, not just in prompts or filters.
Priya Subramaniam·
 MCP Policy and Compliance
FedRAMP Authorization Requirements for AI Agent Infrastructure
Vendors must document AI agent capabilities, identities.
Priya Subramaniam·
 Controlled Unclassified Information
NIST SP 800-171 Controls for AI Agent Access to CUI
Organizations must map AI agent identities and actions to NIST 800-171 controls for assessment.
Priya Subramaniam·
 Third-Party AI Risk
Model Provider Data Handling Commitments Compared
Enterprise contracts bar model training, while consumer plans allow it by default.
Priya Subramaniam·
 Third-Party AI Risk
Contractual Controls for SaaS Integrations Called by AI Agents
SaaS contracts must shift governance controls to vendors as AI agents act without human review.
Priya Subramaniam·
 AI Coding Agents
GitHub Copilot Enterprise vs Third-Party AI Coding Agents
Governance controls, not code quality, determine whether AI coding agents reach production.
Priya Subramaniam·
 MCP Security
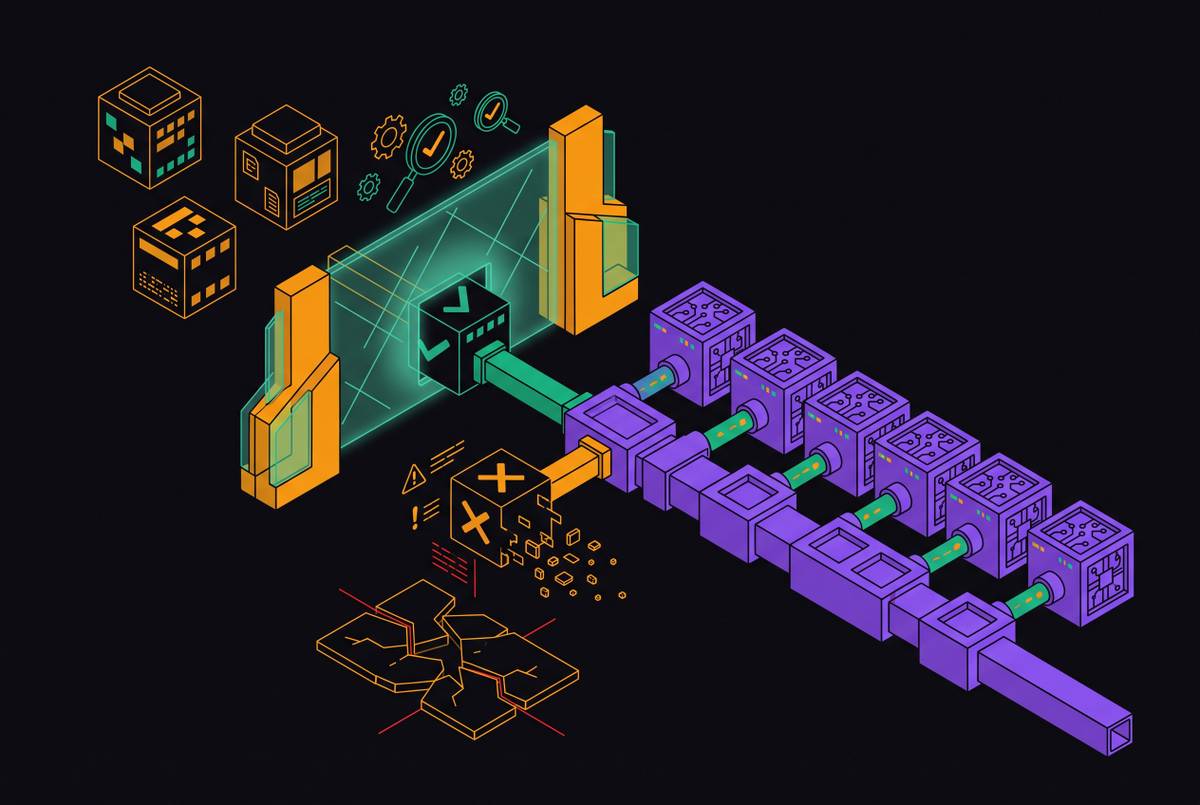
Vetting and Rug Pull Protection for Third-Party MCP Servers in Enterprise Agent Pipelines
MCP servers can turn malicious after approval, exploiting how trust binds to names, not behavior.
Priya Subramaniam·
 Privacy Impact Assessment
PIA vs DPIA Distinctions in Practice
Not every privacy assessment that looks thorough will satisfy legal requirements.
Priya Subramaniam·
 MCP Policy and Compliance
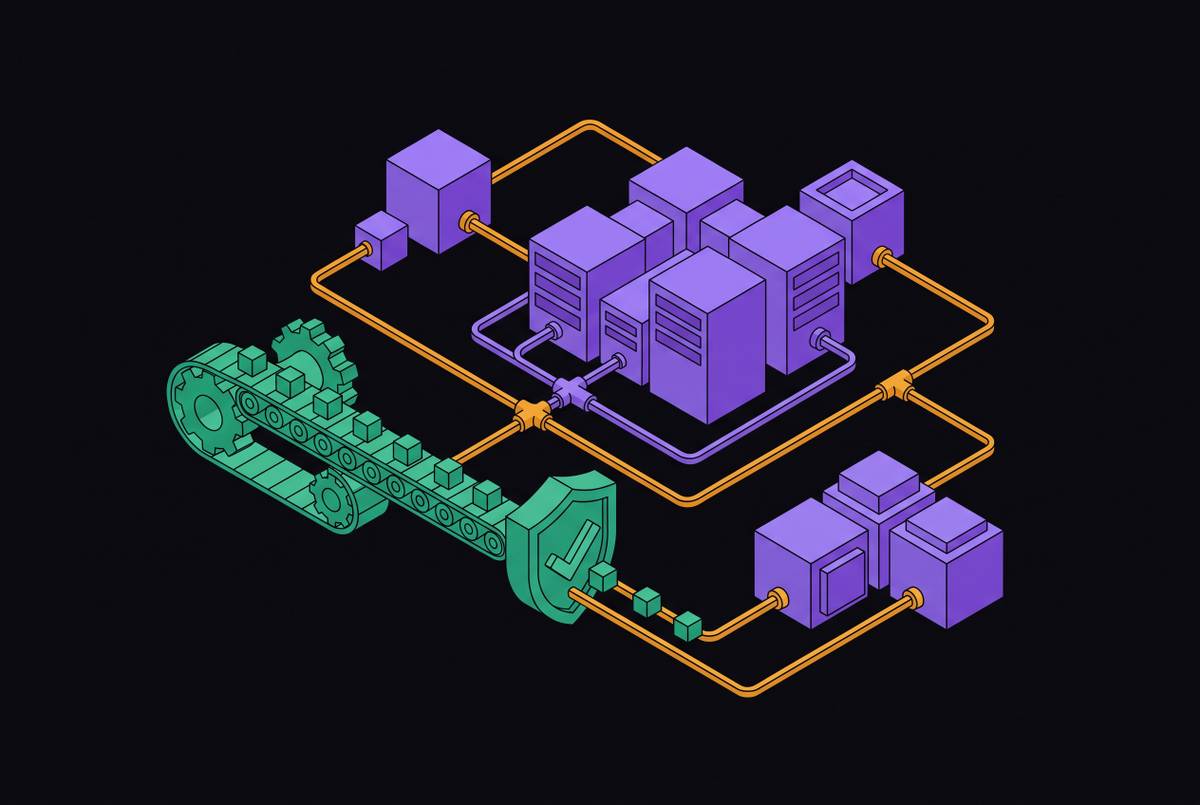
Regulatory Compliance Automation in MCP Deployments
Agents need runtime governance because MCP shifts compliance decisions from code to behavior.
Priya Subramaniam·
 MCP Policy and Compliance
NIS2 Directive Implications for AI-Driven Enterprise Operations
EU regulators are enforcing NIS2 on AI systems whether the directive names them or not.
Priya Subramaniam·
 MCP Policy and Compliance
HIPAA Considerations for AI Agents Accessing Health Data via MCP
Build HIPAA compliance into the MCP server layer itself, not downstream from the model.
Priya Subramaniam·
 MCP Policy and Compliance
SOC 2 Controls for MCP-Enabled AI Environments
Autonomous agents break SOC 2's core assumption that humans control each action.
Priya Subramaniam·
 MCP Policy and Compliance
GDPR Compliance When AI Agents Access Personal Data via MCP
MCP servers expose personal data to unauthenticated access without the lawful bases GDPR demands.
Priya Subramaniam·
 MCP Policy and Compliance
EU AI Act Requirements for Agentic AI Systems
Existing compliance obligations bind agent deployments now, not at the December 2027 deadline.
Priya Subramaniam·
 MCP Security
Prompt Injection Attacks Targeting MCP Tool Calls
Attackers can hijack AI agents by hiding malicious instructions in tool descriptions and content.
Priya Subramaniam·
 MCP Architecture
MCP Tool Schema Design for Least Privilege
Securing MCP servers starts with three schema fields and strict input constraints.
Priya Subramaniam·
 AI Agent Governance
Change Management for Enterprise AI Governance Programs
Most AI governance fails because companies treat it as policy, not change management.
Priya Subramaniam·
 AI Agent Governance
Agentic AI Incident Response Playbooks
Agentic AI demands governance playbooks, not just scripts.
Priya Subramaniam·
 AI Agent Governance
Governance Frameworks for Autonomous AI Agents
Four pillars keep autonomous AI agents from breaking your governance before they break your systems.
Priya Subramaniam·
 AI Agent Governance
Shadow AI and Ungoverned MCP Adoption in Enterprises
Most enterprises have no idea how many AI tools their workers actually use.
Priya Subramaniam·
 Enterprise MCP Deployment
MCP Server Registry Design and Implementation
The registry stores metadata pointers, not binaries, keeping performance lean and governance clear.
Priya Subramaniam·
 AI Agent Governance
RBAC Design for AI Agents in the Enterprise
Human-built RBAC breaks for AI agents, and registered identities come first.
Priya Subramaniam·
 AI Agent Governance
Real-Time Agent Activity Monitoring vs Post-Incident Audit Logs
Live monitoring can halt a rogue agent, while audit logs only explain the damage.
Priya Subramaniam·