OIDC vs SAML for Enterprise Authentication
Security isn't the real issue—architecture and operational fit are.
Marcus Delacroix-Ng
Contributing Analyst, Data & Risk Standards
Marcus Delacroix-Ng worked as a risk consultant for financial-sector clients on data classification and vendor due diligence programs for over twelve years before turning to full-time analysis and writing. His work focuses on the structural standards that organizations need to govern data flowing through automated and agent-driven pipelines.
11 stories
Security isn't the real issue—architecture and operational fit are.
Choosing between local and remote servers sets your security posture before code runs.
Enterprises deploying MCP must choose between access control models the protocol never specified.
How static credentials expose CI/CD pipelines to automated agent attacks.
Security risks that MCP vendors underestimated are forcing the OWASP Top 10 for LLMs to evolve.
MCP servers can be impersonated at runtime because identity gets approved once but never reverified.
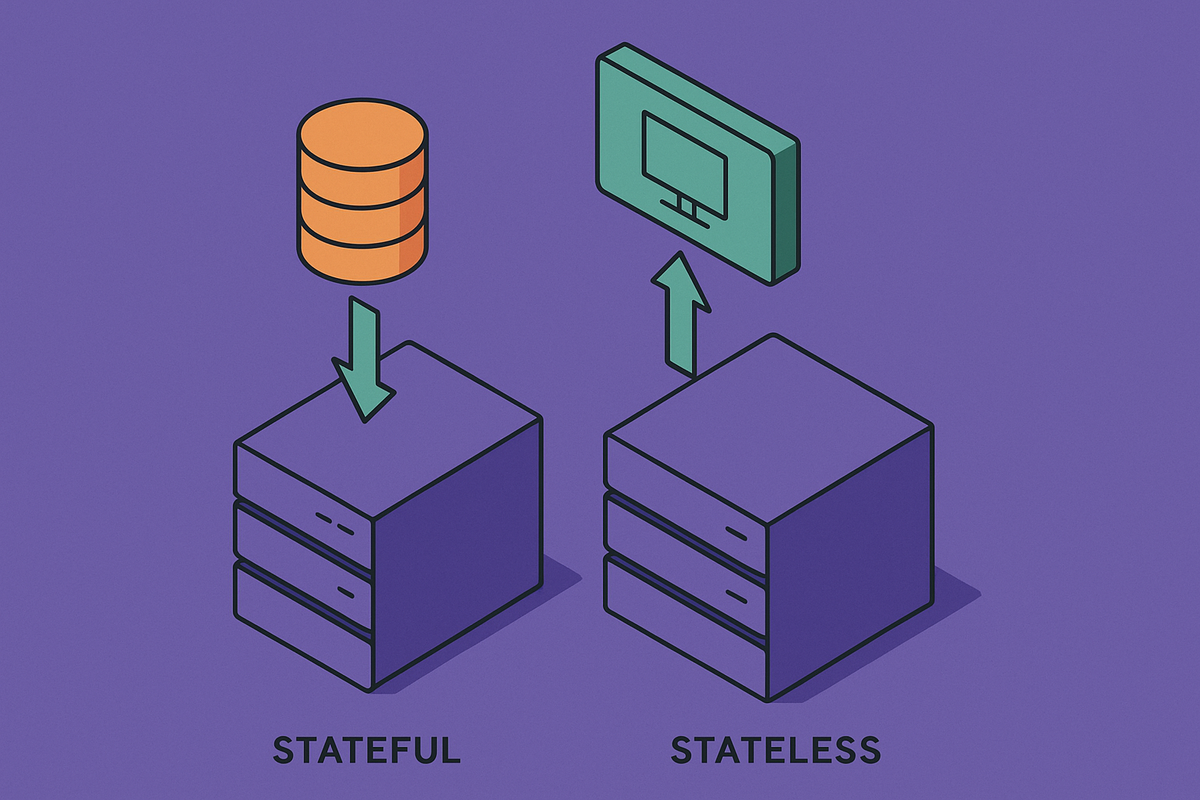
Choosing stateful or stateless shapes how your MCP server scales and handles concurrent users.
Date-based versioning tracks breaking changes only, while features shift independently underneath.
Most enterprises lack the controls to govern AI agents safely in production right now.
Most enterprises are already running ungoverned AI agents they don't know exist.
Early choices in MCP governance are now too costly to reverse.